
Defensive Security & Blue Team BleepingComputer 1 month ago

September Windows Server updates break Remote Desktop Services

CN
CyberNew Threat Research Desk
• Original Reporting: BleepingComputer
CyberNew Threat Intel Assessment
Assessed Severity: MEDIUM
Impacted Surface
Client Endpoints & Operating Systems
Intelligence Sector
Defensive Security & Blue Team

Analyst Takeaway

"Windows admins report that the September 2026 cumulative updates are causing Remote Desktop Services (RDS) failures on Windows Server 2019, 2022, and 2025 systems, preventing users from connecting and, in some cases, requiring a hard reset to restore functionality. The problems appear after installing this month's Microsoft September 2026 Patch Tuesday cumulative updates, with many admins..."

Recommended Defense & Mitigation

  • Threat Monitoring: Ingest published IOCs into SIEM/EDR detection rules for continuous telemetry monitoring.
  • Security Awareness: Alert staff and maintain baseline endpoint hardening across endpoints.
Curated & Verified by CyberNew Threat Intelligence Desk Standard Defense Framework (NIST / MITRE ATT&CK)

Windows admins report that the September 2026 cumulative updates are causing Remote Desktop Services (RDS) failures on Windows Server 2019, 2022, and 2025 systems, preventing users from connecting and, in some cases, requiring a hard reset to restore functionality.

The problems appear after installing this month's Microsoft September 2026 Patch Tuesday cumulative updates, with many admins reporting on Reddit [1, 2, 3] that RDS servers work normally for a few hours before connections start failing.

Once a server starts failing, existing Remote Desktop sessions may not be able to disconnect or log off properly. New connection attempts can also hang during the connection process and eventually fail.
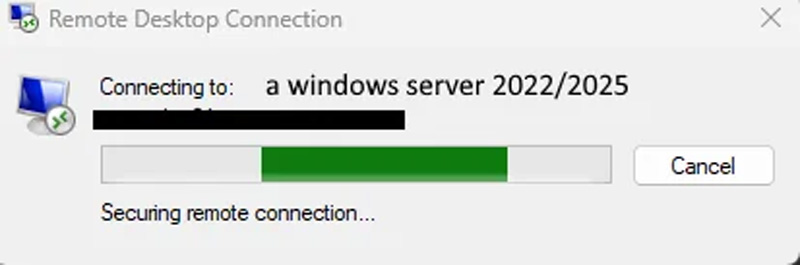
Hanging Remote Desktop connection
Source: Reddit
Save your seat

Source Verification & Original Intelligence

This threat report was reviewed by CyberNew analysts and cross-referenced with primary security disclosures from BleepingComputer.

Primary Advisory →