
Threat Intelligence & APT The Record 1 month ago

Scammer behind $245 million crypto heist pleads guilty to RICO charges

CN
CyberNew Threat Research Desk
• Original Reporting: The Record
CyberNew Threat Intel Assessment
Assessed Severity: INFORMATIONAL
Impacted Surface
Enterprise Perimeter & Network Defense
Intelligence Sector
Threat Intelligence & APT

Analyst Takeaway

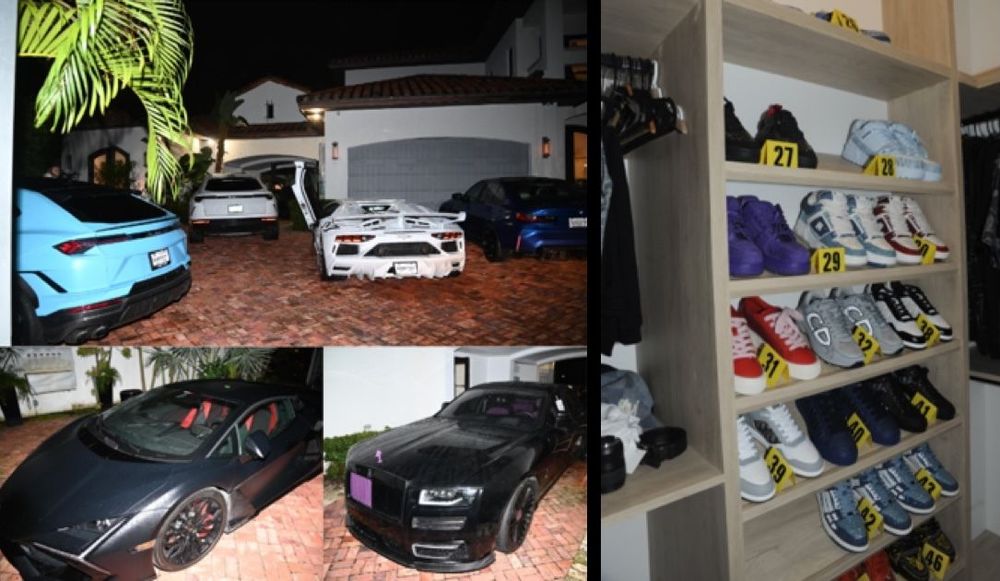
"Cars and sneakers purchased with funds from a fraud ring run by Malone Lam. Image: Department of Justice Scammer behind $245 million crypto heist pleads guilty to RICO charges A Singaporean national pleaded guilty to racketeering charges on Tuesday for his role leading a group of scammers who stole more than $245 million in cryptocurrency. Malone Lam, 22, will appear in U.S. District Court in..."

Recommended Defense & Mitigation

  • Threat Monitoring: Ingest published IOCs into SIEM/EDR detection rules for continuous telemetry monitoring.
  • Security Awareness: Alert staff and maintain baseline endpoint hardening across endpoints.
Curated & Verified by CyberNew Threat Intelligence Desk Standard Defense Framework (NIST / MITRE ATT&CK)
lam malone
Cars and sneakers purchased with funds from a fraud ring run by Malone Lam. Image: Department of Justice

Scammer behind $245 million crypto heist pleads guilty to RICO charges

A Singaporean national pleaded guilty to racketeering charges on Tuesday for his role leading a group of scammers who stole more than $245 million in cryptocurrency. 

Malone Lam, 22, will appear in U.S. District Court in Washington D.C. on December 8 for more information on sentencing. Participating in a RICO conspiracy charges carry sentences ranging from 7 to 20 years. 

Lam was indicted on scamming charges in September 2024 after drawing law enforcement scrutiny for parlaying stolen crypto into lavish Hamptons vacations, cars and private jets. Prosecutors said Lam, known as “Anne Hathaway,” or “$$$,” ran an operation where he and others would conduct social engineering scams to steal cryptocurrency. 

In several incidents, members called crypto holders pretending to be customer service or representatives from Apple and Google, eventually convincing them to hand over key account details that enabled crypto thefts. 

The group gained access to databases of information about people with large amounts of cryptocurrency and either scammed them into providing access to their funds or broke into their homes to physically steal devices.

Source Verification & Original Intelligence

This threat report was reviewed by CyberNew analysts and cross-referenced with primary security disclosures from The Record.

Primary Advisory →