

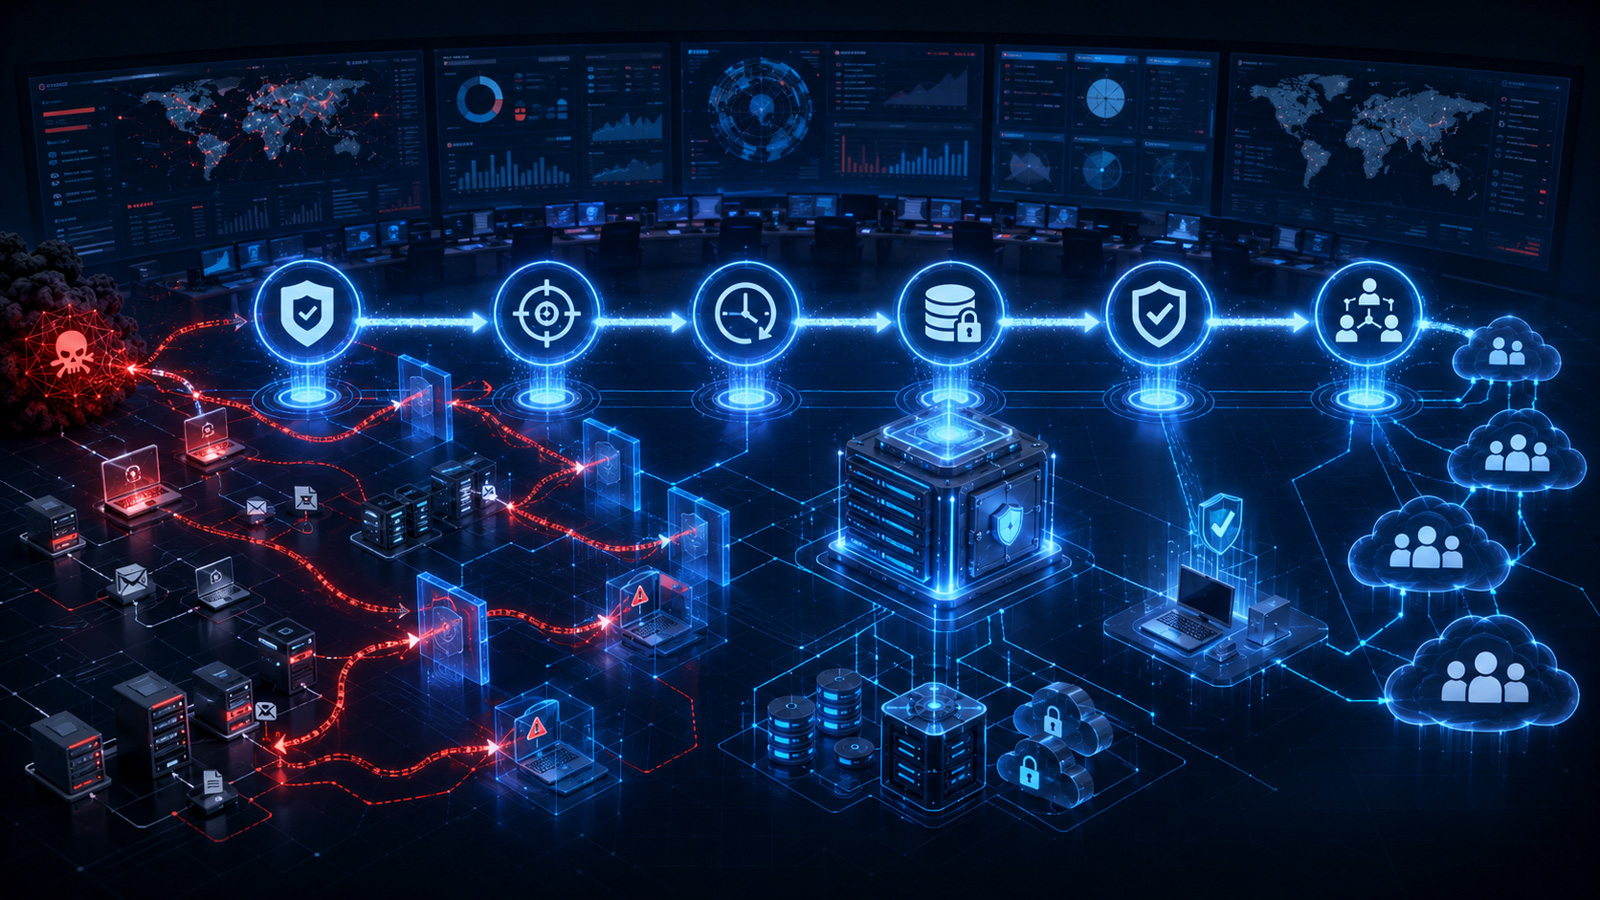
Ransomware protection for MSPs should deliver six tested outcomes: reduce exposure, detect activity before encryption, provide 24/7 response, preserve isolated recovery points, recover cleanly and operate consistently across tenants. Backup alone is not enough, and neither is endpoint detection without a rehearsed recovery path.
The Acronis Cyberthreats Report identified 143 MSP, IT-service provider and telecom ransomware victims in 2025, with phishing accounting for 52% of initial access cases and unpatched vulnerabilities for 27%.
The checklist below turns those failure modes into controls and evidence an MSP should require before calling a service complete.
The six things your service must do and what to verify
A complete ransomware protection service connects prevention, detection, response and recovery. For each control, demand evidence from the exact tenant, workload, storage configuration and service tier being sold.
|
Operational job |
Proof to require |
Acronis capability mapping |
|
1. Reduce exposure |
Set patch SLAs by severity and prove MFA for management portals and remote access. Separate backup and security administration; test that one compromised technician account cannot change protection and delete recovery points. |
Acronis Cyber Protect Cloud provides vulnerability assessment, patch management, URL filtering and role-based administration. Verify the services enabled per tenant. |
|
2. Detect across the attack |
Run a controlled behavioral test and confirm an actionable incident appears before widespread encryption. Check endpoint isolation and the identity, email and Microsoft 365 response actions the client requires. |
Acronis Active Protection and EDR cover endpoint behavior; Acronis XDR adds endpoint, email, identity and Microsoft 365 visibility. |