
Threat Intelligence & APT SecurityWeek 4 weeks ago

NightmareStresser DDoS Service Disrupted in International Operation

CN
CyberNew Threat Research Desk
• Original Reporting: SecurityWeek
CyberNew Threat Intel Assessment
Assessed Severity: INFORMATIONAL
Impacted Surface
Enterprise Perimeter & Network Defense
Intelligence Sector
Threat Intelligence & APT

Analyst Takeaway

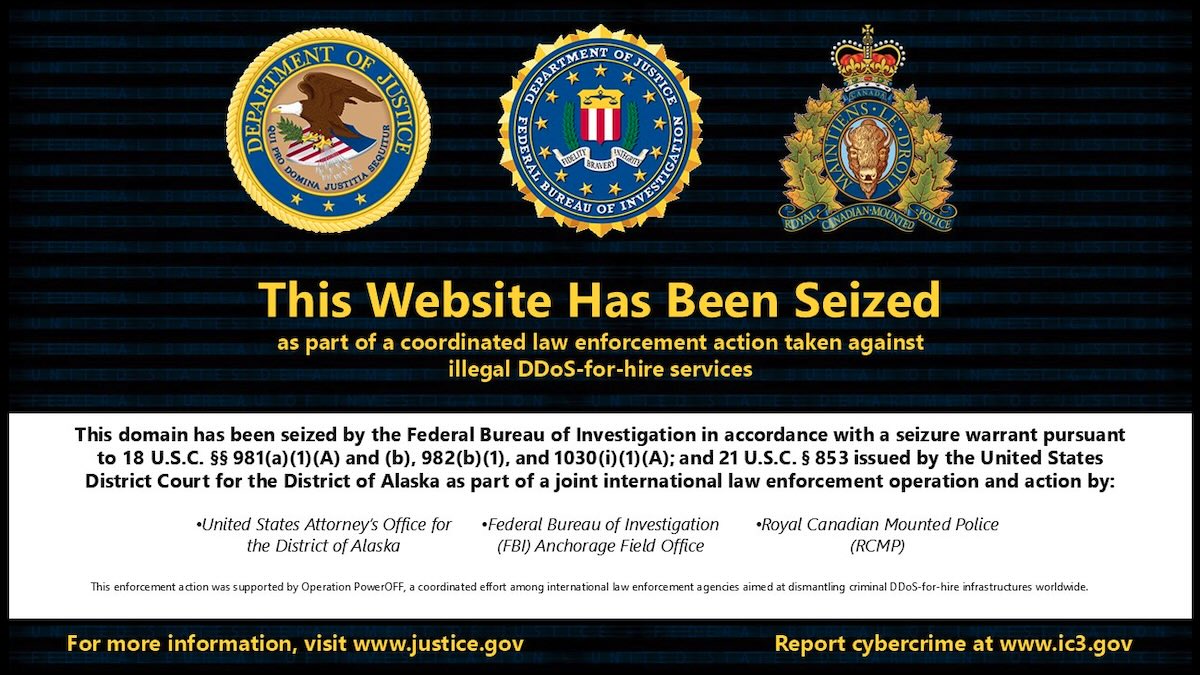
"NightmareStresser, one of the longest-running distributed denial-of-service (DDoS) for-hire services in the world, has been disrupted. The US Department of Justice announced this week that the FBI has seized the internet domains associated with the booter service. Visitors to nightmare-stresser[.]com and nightmarestresser[.]org are now served a seizure banner. Authorities said NightmareStresser..."

Recommended Defense & Mitigation

  • Threat Monitoring: Ingest published IOCs into SIEM/EDR detection rules for continuous telemetry monitoring.
  • Security Awareness: Alert staff and maintain baseline endpoint hardening across endpoints.
Curated & Verified by CyberNew Threat Intelligence Desk Standard Defense Framework (NIST / MITRE ATT&CK)
NightmareStresser DDoS takedown

NightmareStresser, one of the longest-running distributed denial-of-service (DDoS) for-hire services in the world, has been disrupted.

The US Department of Justice announced this week that the FBI has seized the internet domains associated with the booter service.

Visitors to nightmare-stresser[.]com and nightmarestresser[.]org are now served a seizure banner.

Authorities said NightmareStresser had been active since at least 2022 and was used to launch hundreds of thousands of DDoS attacks against victims worldwide.

However, security researcher Alex Carter reported last year that NightmareStresser was likely founded in 2016 and became popular in 2018, after rival services were disrupted, becoming the largest DDoS tool in 2019.

By 2025, it had grown to nearly 1 million users. It could launch between 3,000 and 4,000 attacks per hour, accepted cryptocurrency payments, but avoided government, education, and hospital domains.

Advertisement. Scroll to continue reading.

The NightmareStresser takedown was part of Operation PowerOFF, a coordinated global effort to dismantle DDoS-for-hire infrastructures globally and hold the individuals behind these services accountable.

Written By Ionut Arghire

Source Verification & Original Intelligence

This threat report was reviewed by CyberNew analysts and cross-referenced with primary security disclosures from SecurityWeek.

Primary Advisory →