
Threat Intelligence & APT BleepingComputer 1 month ago

McKesson discloses breach after ShinyHunters claims patient data theft

CN
CyberNew Threat Research Desk
• Original Reporting: BleepingComputer
CyberNew Threat Intel Assessment
Assessed Severity: INFORMATIONAL
Impacted Surface
Enterprise Data & Identity Stores
Intelligence Sector
Threat Intelligence & APT

Analyst Takeaway

"Healthcare and pharmaceutical distribution giant McKesson has disclosed a cybersecurity incident involving unauthorized access to third-party applications and data theft, with the ShinyHunters extortion group claiming it stole 284 million patient data records. McKesson is a major U.S. healthcare company and pharmaceutical distributor that provides medicines, medical supplies, technology, and..."

Recommended Defense & Mitigation

  • Threat Monitoring: Ingest published IOCs into SIEM/EDR detection rules for continuous telemetry monitoring.
  • Security Awareness: Alert staff and maintain baseline endpoint hardening across endpoints.
Curated & Verified by CyberNew Threat Intelligence Desk Standard Defense Framework (NIST / MITRE ATT&CK)

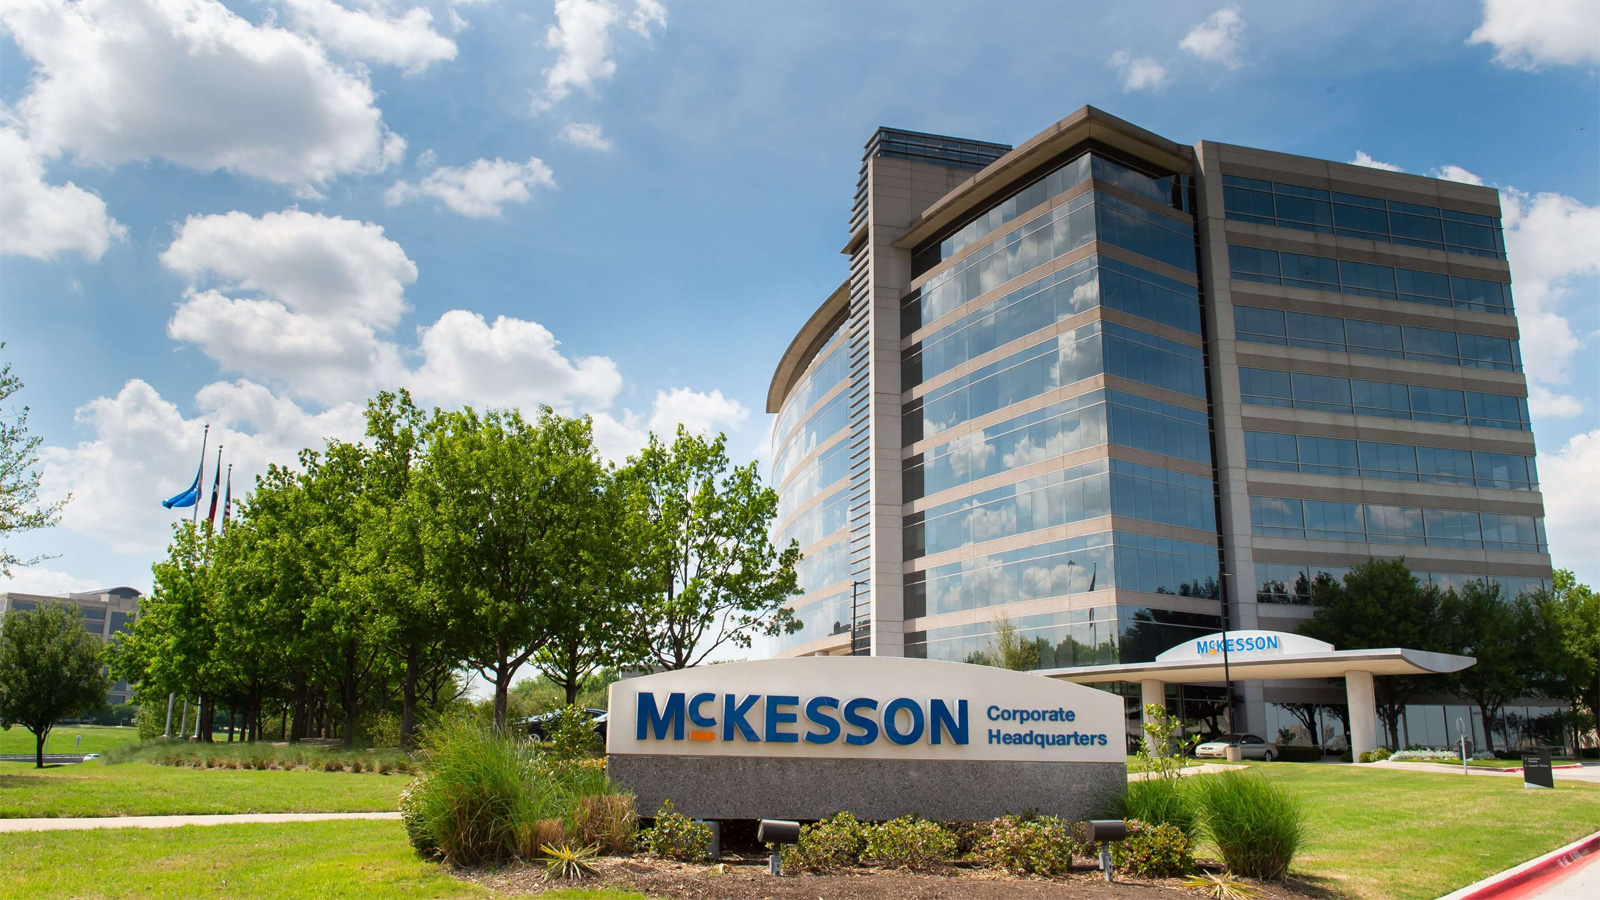
McKesson headquarters

Healthcare and pharmaceutical distribution giant McKesson has disclosed a cybersecurity incident involving unauthorized access to third-party applications and data theft, with the ShinyHunters extortion group claiming it stole 284 million patient data records.

McKesson is a major U.S. healthcare company and pharmaceutical distributor that provides medicines, medical supplies, technology, and services to healthcare providers and pharmacies.

CyberInsider first reported the breach earlier today, and McKesson later disclosed it in a Form 8-K filing with the U.S. Securities and Exchange Commission.
image

McKesson says it discovered the cybersecurity incident on August 25, 2026, and that its investigation remains in the early stages.

"Information about the incident, including any updates, is available on the company's website at www.mckesson.com/cybersecurity," McKesson said in its SEC filing.

"As of the date of this filing, the company has not determined that the incident is material or that the incident has had, or is reasonably likely to have, any material impact on the company, including its financial condition or results of operations."

Get the report

Source Verification & Original Intelligence

This threat report was reviewed by CyberNew analysts and cross-referenced with primary security disclosures from BleepingComputer.

Primary Advisory →