

Cyber News BleepingComputer 4 days ago

Ledger confirms spy chip implant behind wallet crypto thefts

CN
CyberNew Threat Research Desk
• Original Reporting: BleepingComputer
CyberNew Threat Intel Assessment
Assessed Severity: INFORMATIONAL
Impacted Surface
Enterprise Perimeter & Network Defense
Intelligence Sector
Cyber News

Analyst Takeaway

"Ledger has confirmed that some of its devices distributed through Southeast Asian reseller CryptoBilis were compromised with a hardware implant that drained users' cryptocurrency wallets. The company has been investigating reports of users losing funds from wallets purchased through CryptoBilis, a major Malaysia-based hardware wallet retailer operating across Southeast Asia. Some researchers have..."

Recommended Defense & Mitigation

  • Threat Monitoring: Ingest published IOCs into SIEM/EDR detection rules for continuous telemetry monitoring.
  • Security Awareness: Alert staff and maintain baseline endpoint hardening across endpoints.
Curated & Verified by CyberNew Threat Intelligence Desk Standard Defense Framework (NIST / MITRE ATT&CK)

Ledger confirms hardware wallet spy implant behind crypto thefts

Ledger has confirmed that some of its devices distributed through Southeast Asian reseller CryptoBilis were compromised with a hardware implant that drained users' cryptocurrency wallets.

The company has been investigating reports of users losing funds from wallets purchased through CryptoBilis, a major Malaysia-based hardware wallet retailer operating across Southeast Asia.

Some researchers have shown the implant in Ledger X since September 16, saying tampered devices were available for nearly half the price of the original hardware.

Ledger wallets are physical devices designed to securely store the private keys that control cryptocurrency assets and authorize transactions.

On October 9, Ledger said it had launched an investigation into user reports of cryptocurrency losses and asked CryptoBilis to stop selling and shipping Ledger devices.
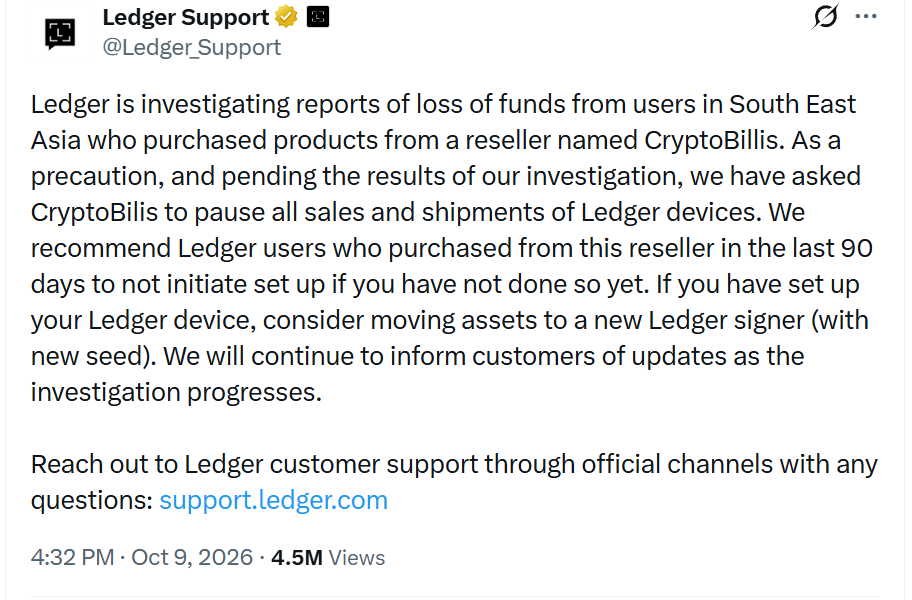
Ledger

The next day, the company confirmed hardware tampering on at least one device, though it’s still unclear exactly how or when the devices were tampered with.

Save your seat

Source Verification & Original Intelligence

This threat report was reviewed by CyberNew analysts and cross-referenced with primary security disclosures from BleepingComputer.

Primary Advisory →