
Threat Intelligence & APT The Record 1 month ago

Healthcare facilities operator Nutex says patient, employee data stolen in August incident

CN
CyberNew Threat Research Desk
• Original Reporting: The Record
CyberNew Threat Intel Assessment
Assessed Severity: INFORMATIONAL
Impacted Surface
Enterprise Perimeter & Network Defense
Intelligence Sector
Threat Intelligence & APT

Analyst Takeaway

"The facade of a Nutex Health specialty hospital in Texas. Image: @nutexhealth / X Healthcare facilities operator Nutex says patient, employee data stolen in August incident Hackers stole patient and employee data from healthcare giant Nutex during a cyberattack announced last week, the company said in regulatory filings on Monday. In an 8-K filing with the Securities and Exchange Commission..."

Recommended Defense & Mitigation

  • Threat Monitoring: Ingest published IOCs into SIEM/EDR detection rules for continuous telemetry monitoring.
  • Security Awareness: Alert staff and maintain baseline endpoint hardening across endpoints.
Curated & Verified by CyberNew Threat Intelligence Desk Standard Defense Framework (NIST / MITRE ATT&CK)
Nutex emergency room
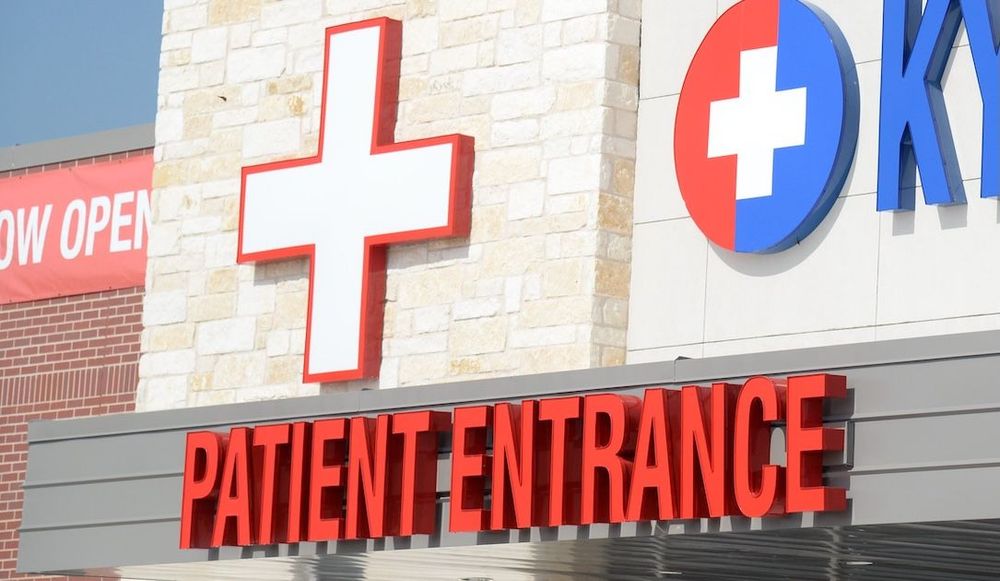
The facade of a Nutex Health specialty hospital in Texas. Image: @nutexhealth / X

Healthcare facilities operator Nutex says patient, employee data stolen in August incident

Hackers stole patient and employee data from healthcare giant Nutex during a cyberattack announced last week, the company said in regulatory filings on Monday. 

In an 8-K filing with the Securities and Exchange Commission (SEC), Nutex said it is being extorted by cybercriminals who broke into the company’s servers and exfiltrated information related to patients, employees and external providers as well as confidential financial data. 

 “The third party has threatened to post such information externally,” Nutex said, adding that it is still investigating how much data was taken and what impact it will have on the company. 

Nutex earned $427.2 million in the first half of 2026 through its operation of 27 hospital and outpatient facilities in 12 states. It also controls a physician network focused on primary care. 

The Houston-based company initially disclosed a cyberattack to the SEC on August 24, warning investors that it hired cybersecurity experts to help address the attack. Monday’s filing notes that after the initial disclosure, a class action complaint was filed in Texas “on behalf of a putative class of all individuals whose personally identifiable information and/or protected health information was allegedly accessed and/or acquired by an unauthorized party in connection with the incident.”

Source Verification & Original Intelligence

This threat report was reviewed by CyberNew analysts and cross-referenced with primary security disclosures from The Record.

Primary Advisory →