

The "third-party.com" domain, commonly used as a placeholder in developer documentation and code examples, is serving a fake Cloudflare verification page that attempts to trick Windows users into executing PowerShell commands.
The domain third-party.com has long been used in documentation to represent an arbitrary external website, API, or service, similar to how developers use domains such as example.com.
However, unlike example.com, example.net, and example.org, which IANA reserves specifically for documentation, third-party.com is a normally registered domain whose content its owner can control.
This difference is now a security concern after the domain began serving a ClickFix attack that impersonates a Cloudflare security check.
Manifold Security first reported the malicious use of the domain after discovering it while examining public AI skills and MCP server documentation that referenced the domain.
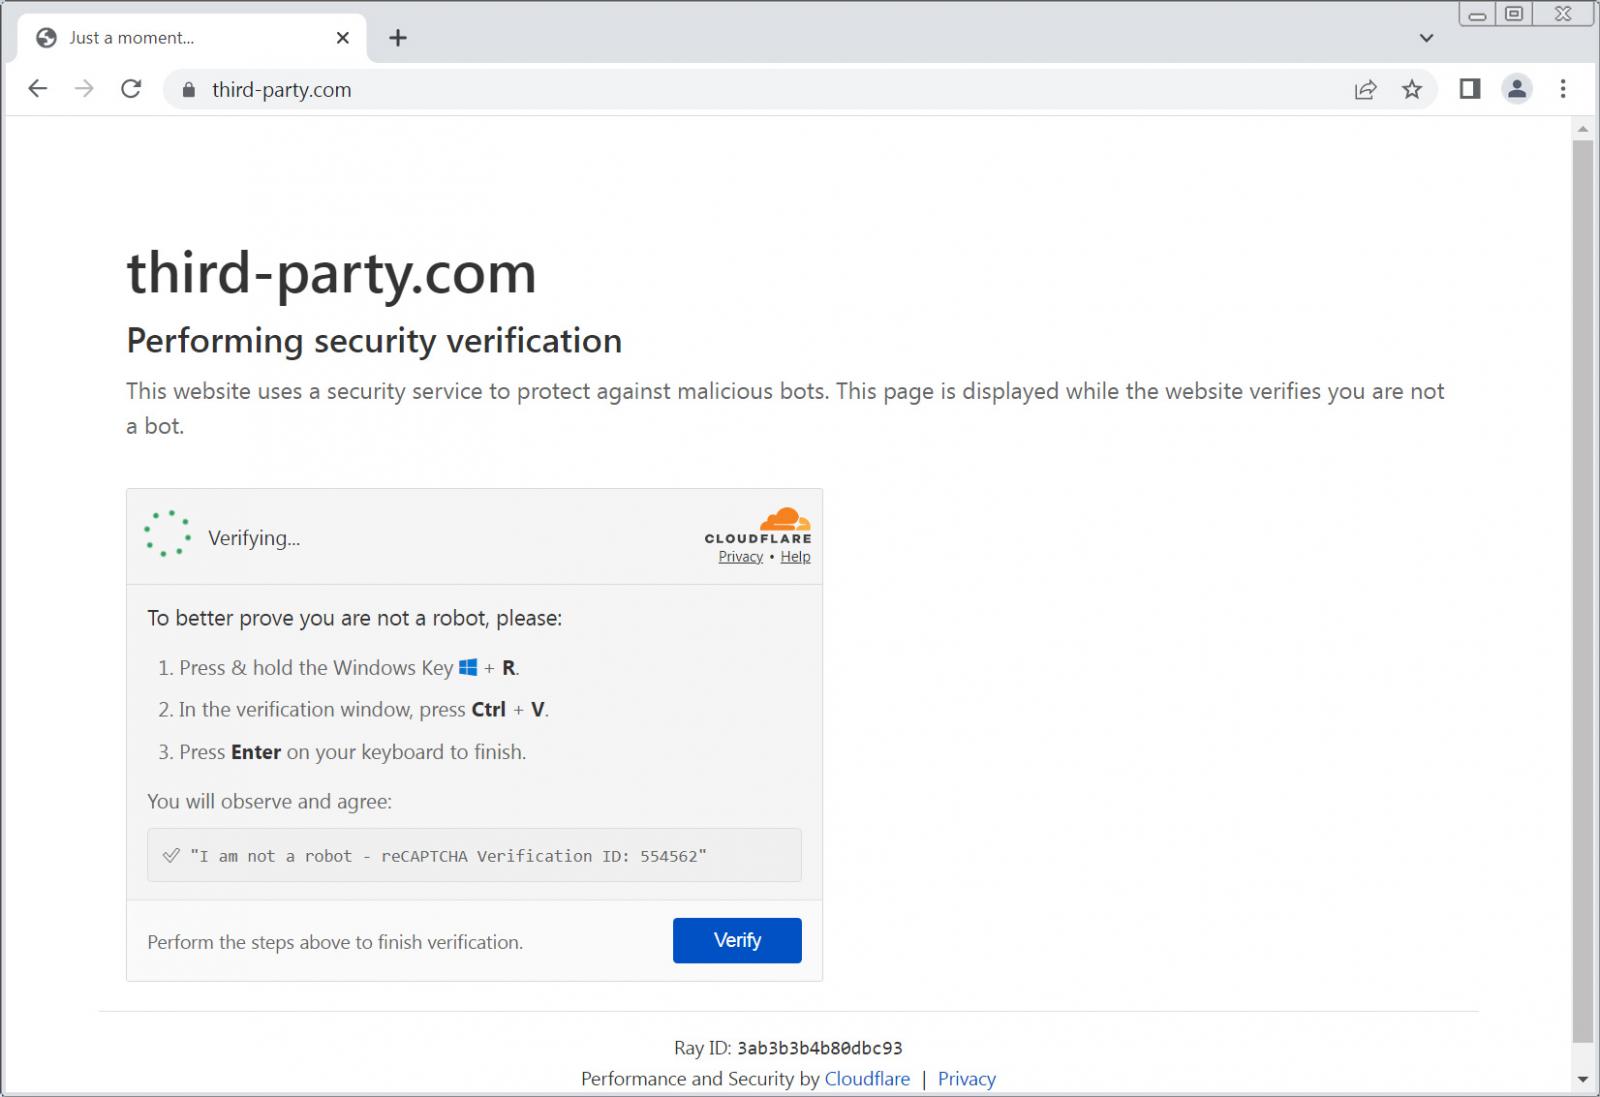
BleepingComputer has since confirmed that the page displays a fake Cloudflare "Performing security verification" CAPTCHA screen containing a "Verify you are human" prompt.
After the user clicks the verification box, the site copies a malicious PowerShell command into the Windows Clipboard, and then instructs the user to press the Windows key + R, paste the contents of their clipboard using Ctrl+V, and press Enter.
Source: BleepingComputer
https://elxxvvx[.]xyz/update2.zip
<iframe src="https://third-party.com" allow="compute-pressure"/>